Sessions
Date, delivery mode, trainer and fee are specific to each session. Fees are per person.
Request a quote for a date for your organisation or for the next run.
Application formNo membership required
Get a quote
Training content
Overview
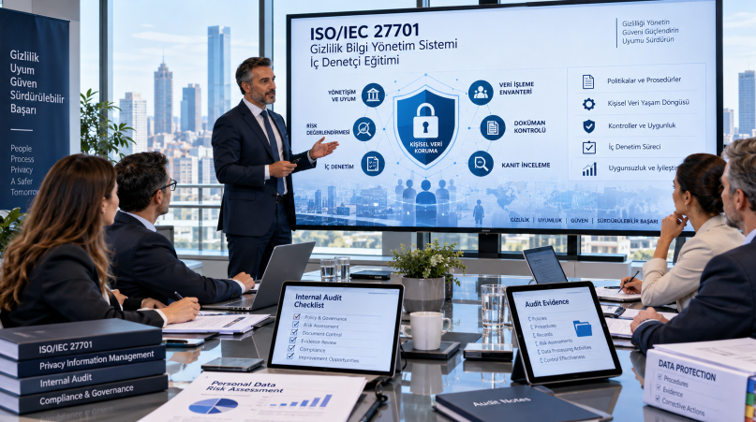
ISO/IEC 27701 Privacy Information Management System Internal Auditor Training has been designed to provide the knowledge and auditor skills required to evaluate the effectiveness of the Privacy Information Management System (PIMS) and to plan, conduct, report and follow up internal audits in accordance with the requirements of ISO/IEC 27701:2025.
The language of the training is Turkish. The training is delivered online.
About the Training
The training covers the structure of the ISO/IEC 27701:2025 standard, PIMS requirements, the obligations of PII controllers and processors, privacy risk management, the personal data lifecycle, privacy controls, ISO 19011 auditing principles, audit planning, the collection of objective evidence, the identification of nonconformities and the follow-up of corrective actions.
Who Should Attend?
- ISO/IEC 27701 internal auditors and auditor candidates
- PIMS managers and team members
- Information security and privacy personnel
- Employees involved in KVKK/GDPR processes
- Risk and compliance personnel
- ISO/IEC 27001 internal auditors
- Data protection and information technology personnel
- Management system officers
- Professionals who will be involved in internal audit activities
Objectives and Outcomes
The aim is to enable participants to interpret the requirements of ISO/IEC 27701:2025 correctly, evaluate PIMS processes using a risk-based approach and objective evidence, and conduct internal audits in accordance with ISO 19011 principles.
By the End of the Training
Participants will be able to:
- Interpret the requirements of ISO/IEC 27701:2025.
- Evaluate the scope and core processes of the PIMS.
- Audit the requirements for PII controllers and PII processors.
- Review privacy risk assessments.
- Evaluate the PII lifecycle and privacy controls.
- Define the scope, criteria and plan for an internal audit.
- Collect and evaluate objective audit evidence.
- Apply audit interviewing and sampling techniques.
- Document nonconformities accurately and objectively.
- Monitor the implementation and effectiveness of corrective actions.
Programme and Method
Training Topics
- ISO/IEC 27701:2025 Standard and PIMS Requirements
- Responsibilities of PII Controllers, Processors and Privacy Officers
- Privacy Risk Management and the PII Life Cycle
- Privacy Controls, Data Subject Rights and Third-Party Management
- Integration of PIMS with ISO/IEC 27001
- ISO 19011 Internal Audit Principles and Auditor Competence
- Planning the Internal Audit and Determining its Scope and Criteria
- Conducting the Audit, Interviewing, Sampling and Objective Evidence
- Audit Findings, Writing Non-conformities and Reporting
- Follow-up of Corrective Actions and Evaluation of Audit Effectiveness
Training Method
The training is delivered through subject presentations, evaluation of ISO/IEC 27701 requirements, privacy risk scenarios, examples of PII processing, audit planning exercises, objective evidence assessments, case studies and non-conformity writing exercises.
Attendance and Certificate
Certification Rule
A certificate of attendance is issued to all participants whose attendance has been confirmed. To receive a certificate of achievement, participants must obtain a passing grade in the examination at the end of the training; participants who use all their examination attempts but do not pass will be issued a certificate of attendance.
FAQ and Resources
Who is the ISO/IEC 27701 Privacy Information Management System Internal Auditor Training suitable for?
It is intended for personnel who will conduct internal audits under ISO/IEC 27701, PIMS team members, information security and privacy specialists, risk and compliance personnel, and professionals involved in data protection processes.
What is the main objective of the training?
To enable participants to evaluate ISO/IEC 27701 requirements systematically and objectively and conduct effective PIMS internal audits.
Which areas are evaluated during an internal audit?
The PIMS scope, privacy risks, PII processing activities, data controller and data processor obligations, privacy controls, data subject rights, third parties, incident management and continual improvement processes are evaluated.
Is the training practical?
Yes. The training includes audit planning, privacy control assessments, objective evidence gathering, interview techniques, case studies and nonconformity writing exercises.
Is there an examination at the end of the training?
Yes. An assessment examination is administered at the end of the training.
References
- ISO/IEC 27701:2025 Privacy Information Management Systems — Requirements and Guidance
- ISO/IEC 27001 Information Security Management Systems
- ISO/IEC 27002 Information Security Controls
- ISO/IEC 29100 Privacy Framework
- ISO 19011 Guidelines for Auditing Management Systems
- KVKK, GDPR and relevant data protection legislation
Similar trainings
EXEMPLAR002ISO/IEC 27701 Privacy Information Management System Transition Training8 hours · No session plannedEXEMPLAR017ISO/IEC 27019 Information Security, Cybersecurity and Privacy Protection Awareness Training8 hours · No session plannedEXEMPLAR018ISO/IEC 27019 Information Security, Cybersecurity and Privacy Protection Internal Auditor Training16 hours · No session planned